Quick Answer
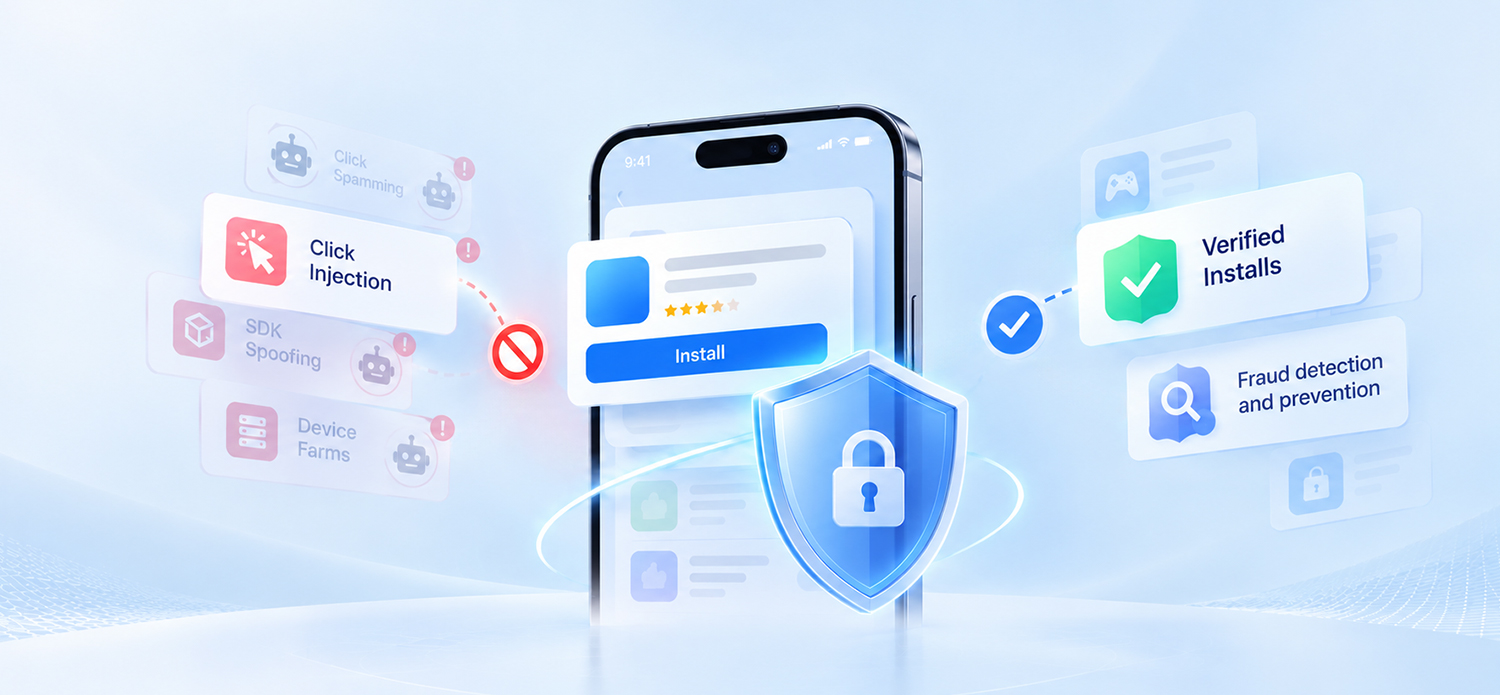
Mobile ad fraud is the deliberate manipulation of mobile advertising activity, installs or attribution to generate illegitimate payouts or claim credit for conversions that a campaign did not genuinely produce. Common forms include click injection, click spamming, SDK spoofing and fake installs.
According to AppsFlyer’s State of Fraud for Marketers 2026 report, organic traffic accounted for 52% of all fraudulent mobile app installs identified in its analysis of 106.4 billion installs across 246,000 apps from Q1 2025 to Q1 2026. This refers to the share of fraudulent installs attributed to organic traffic, not the percentage of organic installs that were fraudulent. The finding highlights why advertisers should examine organic and paid acquisition data when investigating unusual activity.
Introduction
Mobile app install fraud can drain marketing budgets while distorting attribution metrics and forcing growth teams to pay for non-existent or misattributed user conversions. Securing your user acquisition budget requires understanding how invalid traffic operates and enforcing appropriate prevention measures across the campaign workflow. Fraud prevention should therefore be part of a wider mobile user acquisition strategy, with campaign quality assessed alongside install volume and cost.
Invalid traffic (IVT) is a broader category of traffic that does not represent valid advertising activity under the applicable measurement or campaign rules. It can include both deliberate fraud and certain accidental or non-malicious interactions. Mobile ad fraud refers more specifically to intentional manipulation for illegitimate gain. Distinguishing the two helps advertisers investigate suspicious traffic without automatically classifying every reporting anomaly as fraud.
Common Fraud Types in Mobile UA
Fraud tactics vary in how they manipulate attribution, generate non-genuine installs or imitate legitimate user behaviour. Understanding these mobile ad fraud methods helps advertisers distinguish between attribution hijacking and fake or automated activity.
1. Click Injection
Click injection is a form of attribution hijacking primarily associated with Android environments. Malicious apps running in the background may detect when a user initiates a legitimate app download and attempt to trigger a fraudulent ad click around the time the installation completes, claiming credit for a conversion they did not generate. Learn more about click injection and how it can affect mobile attribution.
2. Click Spamming
Click spamming involves generating or reporting ad clicks without genuine user engagement in an attempt to claim attribution for installs that may have occurred organically or through another source. Unlike click injection, which attempts to insert a fraudulent click at a specific point in the installation process, click spamming can generate large volumes of clicks over time. Unusual click volumes, long click-to-install time distributions and weak conversion patterns may warrant investigation, but these signals should be assessed alongside other traffic-quality data.
3. SDK Spoofing
SDK spoofing involves fabricating install or post-install event signals so that an attribution or measurement platform records activity that did not originate from a genuine user journey. This can involve simulated device environments, manipulated requests or other techniques that generate events without a legitimate app interaction.
4. Device Farms, Emulators & Botnets
Physical warehouses or software-based environments can run automated routines across large numbers of devices. These setups download apps, generate synthetic user interactions, reset advertising IDs and repeat the cycle to generate CPI payouts from non-genuine installs.
Warning Signs in Your Install Data
Spotting suspicious activity before it drains your budget requires continuous monitoring of post-install performance data. Sudden spikes in volume accompanied by broken user retention curves can signal invalid traffic.
- Abnormal CTIT patterns: Large clusters of installs occurring within unusually short time windows can signal click injection, while unusually long CTIT distributions may indicate click spamming or other attribution manipulation. CTIT should be evaluated alongside source, device, engagement and post-install signals rather than used as a standalone indicator.
- Low Post-Install Engagement: High install volume combined with unusually weak activation, retention or downstream events can indicate incentivized, automated or otherwise low-quality traffic. These signals should be investigated alongside source, device and attribution data.
- Unusual Device & OS Distributions: Unexpected concentrations of specific devices, OS versions, IP ranges or geographic combinations can warrant investigation, particularly when they coincide with abnormal engagement or conversion patterns.
- Attribution & Reporting Discrepancies: Inconsistencies between your internal analytics tools and ad network reports regarding install timestamps or geo-location tags can require further investigation. These discrepancies do not necessarily indicate malicious activity and should first be reconciled against differences in attribution windows, reporting methodologies, time zones and event definitions.
Important: No individual metric proves invalid activity. Low retention, unusual CTIT patterns or unexpected device distributions can also result from poor targeting, misleading creative, weak onboarding or market-specific user behavior. Investigations should therefore combine multiple signals before traffic is classified as invalid.
How Inventory Quality Can Reduce Exposure
Industry frameworks and supply-chain controls can help advertisers establish greater transparency around inventory sources. For example, app-ads.txt allows app publishers to declare authorized sellers of their advertising inventory, helping buyers verify whether sellers are authorized. These checks improve supply-chain transparency but do not guarantee that inventory is free from invalid traffic or fraud. Measurement and verification standards can provide additional controls around traffic quality and ad delivery.

Alt text: Comparison table of curated direct inventory and open programmatic inventory across supply path, placement control, traffic quality, brand safety, and measurement.
Using verified channels such as OEM inventory alongside carefully evaluated in-app placements can help improve inventory transparency and reduce exposure to low-quality or invalid traffic. For a deeper breakdown of selecting high-quality channels, read our guide on OEM Advertising vs In-App Advertising.
Common MMP-Based Detection Controls
Mobile Measurement Partners provide a central layer for attribution and campaign measurement, while many platforms also offer detection capabilities. Depending on the platform, MMPs may use pre-attribution and post-attribution signals to identify or filter suspicious activity.
Key MMP prevention mechanisms include:
- Click & Attribution Anomaly Detection: Identifying unusual click, install and attribution patterns that may indicate manipulation.
- Device & IP Signals: Flagging suspicious device, IP, proxy, data-center or geographic patterns.
- CTIT Analysis: Examining unusual click-to-install distributions alongside other signals.
- Post-Install Validation: Evaluating whether attributed installs generate expected engagement, events, retention or revenue.
- Known Pattern Detection: Comparing traffic against known indicators of fraudulent or automated activity.

Alt text: Mobile ad fraud prevention infographic showing traffic source verification, post-install quality monitoring, supply-chain controls, MMP-based attribution, anomaly detection, and multiple fraud signals.
How to Prevent Mobile Ad Fraud
1. Vet Your Traffic Sources
Evaluate publishers, supply paths, placements and traffic quality before scaling spend.
2. Use MMP-Based Attribution
Centralize attribution and use available detection signals to identify suspicious installs and events.
3. Monitor Post-Install Quality
Don’t optimize solely toward installs. Track activation, retention, downstream events, revenue and other meaningful outcomes.
4. Investigate Anomalous Cohorts
Segment traffic by source, campaign, device, OS, geography and placement to identify unusual patterns.
5. Use Supply-Chain Controls
Use mechanisms such as app-ads.txt and authorized-seller information where applicable to improve inventory transparency.
6. Combine Multiple Signals
Treat CTIT, device patterns, IP signals, attribution anomalies and post-install behavior as a combined detection framework rather than relying on one metric.
FAQs
What Is the Difference Between IVT and Ad Fraud?
Invalid traffic (IVT) includes all non-human or unintentional ad interactions, such as accidental clicks or search crawler traffic. Ad fraud is a form of invalid traffic in which activity is deliberately designed to manipulate advertising or attribution systems, typically for financial gain.
How Does Click Injection Steal Attribution Credit?
Click injection is primarily associated with Android attribution environments, where malicious apps can attempt to trigger fraudulent clicks around the time a legitimate app is being installed.
Can Ad Fraud Happen on iOS Campaigns?
Yes. While Apple’s privacy and attribution frameworks have changed how certain types of mobile measurement work, iOS campaigns can still face risks such as attribution manipulation, fake installs, SDK spoofing and other forms of invalid activity. Detection should therefore consider source, device, attribution and post-install signals rather than assuming any platform is completely risk-free.
What Are the Most Common Types of Mobile Ad Fraud?
Common types include click injection, click spamming, SDK spoofing, fake or automated installs, device-farm activity, incentivized activity and other forms of attribution manipulation. The exact techniques and signals can vary by platform and campaign setup.
How Can Advertisers Detect Fraudulent App Installs?
Advertisers can look for abnormal CTIT patterns, unusual device or IP distributions, unexpected geographic concentrations, weak post-install engagement, poor retention, source-level anomalies and suspicious attribution patterns. MMP detection signals and independent traffic-quality analysis can provide additional validation. No single metric should be treated as proof of invalid activity.
Does OEM Advertising Eliminate Mobile Ad Fraud?
No. OEM advertising can offer more controlled inventory environments and direct relationships, but no acquisition channel should be treated as completely risk-free. Advertisers should combine inventory controls with MMP-based attribution, traffic-quality monitoring and post-install analysis.
Build App Acquisition Campaigns With AppLabs
AppLabs supports app acquisition across OEM and in-app environments. Explore the AppLabs App Discovery Platform to learn more about its app discovery and campaign capabilities, or contact our team to discuss your acquisition requirements.